TIMEWELL
Solutions
Free ConsultationContact Us
TIMEWELL

Unleashing organizational potential with AI

ISO/IEC 27001 (ISMS) certification mark (SGS / ISMS-AC)

ISO/IEC 27001:2022 certified Certificate No. JP26/00000255 Scope: Planning, development and operation of SaaS products utilizing AI technology

Services

  • ZEROCK
  • TRAFEED
  • TIMEWELL BASE
  • WARP
  • WARP 1Day
  • WARP NEXT Corporate
  • WARP BASIC
  • WARP ENTRE
  • Alumni Salon
  • WARP for Schools
  • Alumni Ventures
  • FDE
  • AI Consulting
  • EMC GLOBAL

Company

  • About Us
  • Team
  • Why TIMEWELL
  • News
  • Contact
  • Free Consultation

Content

  • Insights
  • Knowledge Base
  • Case Studies
  • Whitepapers
  • Events
  • Solutions
  • AI Readiness Check
  • ROI Calculator

Legal

  • Privacy Policy
  • Manual Creator Extension
  • WARP Terms of Service
  • WARP NEXT School Rules
  • Legal Notice
  • Security
  • Anti-Social Policy
  • ZEROCK Terms of Service
  • TIMEWELL BASE Terms of Service

Newsletter

Get the latest AI and DX insights delivered weekly

Your email will only be used for newsletter delivery.

© 2026 株式会社TIMEWELL All rights reserved.

Contact Us
HomeColumnsAIセキュリティISO/IEC 27001 Certification Complete Guide — Stage 1 Through Surveillance: Where Teams Trip on the Full Path
AIセキュリティ

ISO/IEC 27001 Certification Complete Guide — Stage 1 Through Surveillance: Where Teams Trip on the Full Path

Published2026-05-20Updated2026-07-06Ryuta Hamamoto
AI SecurityISO/IEC 27001ISMS CertificationInternal AuditManagement ReviewWARP SECURITY

A chronological walkthrough of ISO/IEC 27001:2022 certification—Stage 1, Stage 2, surveillance, and year-3 recertification.

ISO/IEC 27001 Certification Complete Guide — Stage 1 Through Surveillance: Where Teams Trip on the Full Path
Share

Hello, this is Ryuta Hamamoto from TIMEWELL.

“Stage 1 is in two weeks. What else do we do?” When supporting certification, I always get that question. The earlier ISMS intro (What is ISMS?) covered the big picture. This piece is what happens at each step of the real certification process—and where teams fall.

ISO/IEC 27001:2022 is the baseline for all new certifications after the transition deadline from the 2013 edition ended October 31, 2025 (see JIPDEC). This article assumes May 2026 practice.

Certification lifecycle — the 3-year cycle

Year Audit type Content Effort (mid-size firm)
Year 1 Initial certification (Stage 1+2) Document + on-site 3–5 auditor-days
Year 2 Surveillance Sample controls + PDCA check 2–3 auditor-days
Year 3 Surveillance + recertification Full control re-evaluation 3–4 auditor-days

Stage 1 to Stage 2 is usually 1–3 months. Fix Stage 1 nits before Stage 2—the classic path.

Executives who think “once certified, it gets easy” have it backward. The three-year cycle after go-live is the main event. Serious surveillance findings can suspend or withdraw the certificate. I have seen year-2 surveillance nearly derail a site because “training records only exist for year one.”

Stage 1 — five document-review focus points

Stage 1 is document-heavy (on-site or remote), half day to one day. Focus:

1. Scope validity
Scope document must name org units, sites, processes, and information assets. A third party must see clear boundaries—“contracted development at XX Co.” style.

2. Policy alignment
Top-management signed approval; policy content linked to business issues. Template reuse shows here.

3. Risk assessment process and Statement of Applicability
Methodology documented; SoA lists all 93 Annex A controls as applicable / not applicable with reasons. SoA is among the most important documents.

4. Risk treatment plan
Accept / reduce / transfer / avoid—written.

5. Internal audit and management review evidence
At Stage 1 you generally need at least one of each already done. Last-minute paper trails get spotted in minute quality.

A common field failure: thin “not applicable” reasons. For A.6.7 (remote working) writing only “no such work” collapses when the auditor asks whether a remote-work ban policy exists and whether anyone actually works from home.

AI Security training, taken seriously

A 2-day intensive course fully aligned with OWASP, NIST, ISO/IEC 42001, and METI. Take it as executives, practitioners, or both.

Book a WARP SECURITY ConsultationView Course Details

Stage 2 — what they look at on site

Stage 2 is on-site (hybrid common), 2–4 days.

Day 1: Opening + top-management interview
Plan confirmation and direct interview of leadership—“What is your top information security risk?” “How much budget do you put into ISMS?” I know firms that put a proxy when the CEO was away and had to redo Stage 2.

Middle days: Department interviews and walkthroughs
IT, HR, admin, engineering, sales in scope. Server-room / archive access logs, screen-lock settings, secure disposal—in the flesh.

Final day: Findings draft and closing
Nonconformities and observations shared formally at closing.

Typical Stage 2 findings:

  1. Training coverage gaps: new hires trained; mid-career hires, temps, on-site contractors not
  2. Access reviews missing: leaver accounts still live
  3. Hollow management review: minutes say “no objection” with no leadership decision trail
  4. No supplier evaluation: contracts exist; annual security reviews do not
  5. Suspected backfilled records: Excel education logs with visible last-minute edit history

If I had to pick one Stage 2 risk I see most, it is the leadership interview. Documents can look fine. A CEO who cannot name the top risk in their own words is a different problem.

Surveillance and recertification — “certified and done” is the riskiest posture

Surveillance once a year samples the scope, follows prior findings, and samples controls. An observation left open often upgrades to a nonconformity next year.

Year-3 recertification is near initial-cert volume: all controls re-evaluated; three years of records on the table. Scattered files create a “year-three hell.” From year one I recommend strict record directory structure and naming.

Major nonconformities I have seen in surveillance:

  • Risk assessment never refreshed after year one (related to planning/risk requirements)
  • Internal auditor was the IT security manager auditing their own department (independence failure)
  • Management review skipped two years running (leadership / review requirements)

All can lead to suspension risk.

Cost and effort reality — mid-size case study

What executives care about most. Typical mid-size firm (200–500 employees, ~50 in scope):

Year-one total: ¥3.8–6.0M

Item Ballpark
Consulting ¥2.0–3.5M
Certification body (Stage 1+2 + registration) ¥1.2–1.8M
Internal effort (0.5 FTE × 6 months) ¥0.6–1.0M equivalent

Annual maintenance after year one: ¥1.0–1.8M

Item Ballpark
Certification body (surveillance) ¥0.6–1.0M
Internal maintenance effort ¥0.4–0.8M equivalent

Plus internal training content, external courses, internal auditor credentials (CISA, ISMS auditor trainee, etc.).

In my experience, more than half of teams that “cut consulting and go solo” call a consultant in a panic just before Stage 1. Starting with a seasoned partner often lowers total cost—not sympathy for IT, pure economics.

Also readDoes Blocking Foreign Traffic Work? What Japan's Residential Proxy Data Shows

WARP SECURITY — clearing the last wall before audit

Many readers will feel Stage 2 interview prep is the anxiety peak. The most common TIMEWELL ask: “Documents are ready. Will leadership freeze in interviews?”

WARP SECURITY is an implementation-lab program for the last ~two months before certification—two days of applied drills:

  • Writing SoA correctly — how to justify “not applicable” with confidence across 93 controls
  • Management review scripts — 30 minutes that produce next-quarter priorities, not rubber stamps
  • Stage 2 interview Q&A — ~20 real auditor question patterns rehearsed against your firm
  • Interpreting new controls under AI use — placing ChatGPT-class tools under A.5.23 (cloud) and A.8.28 (secure coding)

That last point is the one I care about most. ISO/IEC 27001:2022 locked before ChatGPT’s mass adoption. Reading clauses literally does not yield modern AI-risk interpretation. WARP SECURITY bridges standard text and current AI threats hands-on.

Details: WARP SECURITY.

Latest as of July 2026

Because ISO/IEC 27001:2022 predated mass generative AI, AI-related control interpretation is supplemented from external guidelines. As of July 2026, a primary reference is AI Business Guidelines v1.2 published March 31, 2026 by MIC/METI (METI). Citing such guidance when generative AI appears in risk assessment and SoA tends to make auditor explanations land more cleanly—my current view. For control design of AI use itself: Governed enterprise AI agents.

Key takeaways — make certification a start, not an end

  • 3-year cycle; surveillance and recertification test field strength more than Stage 1+2
  • Stage 1 focus: scope, policy, risk assessment, SoA, internal audit records—template reuse gets caught
  • Stage 2 core: direct top-management interview and department walkthroughs—avoid proxy-only leadership
  • Year-one total for mid-size often ¥3.8–6.0M; maintenance ~¥1.0–1.8M/year
  • 2022 new controls (A.5.7, A.5.23, A.8.11, A.8.12, A.8.23, A.8.28, etc.) need AI/cloud-era interpretation

I want certification positioned as the starting line where security operations catch a global baseline, not a finish line. The gap between “thinner than year one” at recertification and “operations exceed the standard” is set in the first six months’ seriousness. Build the record habit before you celebrate the certificate.

Related: ISMS beginner’s guide, ISO/IEC 42001 AIMS beginner’s guide, ISMAP explained.
References

  • JIPDEC: Audit points for ISO/IEC 27001:2022 transition
  • Ninsho Partner: How to run ISMS internal audit and checklist
  • GC Consulting: ISO/IEC 27001:2022 management review practice
  • SecureNavi: ISO 27001 audit flow and cost ranges
  • JMAQA: ISO27001 internal audit

This article was produced with the help of AI. A human verified the primary sources and edited the text before publication.

Read next

Articles that answer the question you are likely to have next.

  1. 1What Is ISMS? The Big Picture for Junior Staff Who Just Got “Told to Get ISO/IEC 27001”ISMS (Information Security Management System) certifications in Japan exceeded 8,333 as of May 2026.
  2. 2Does Blocking Foreign Traffic Work? What Japan's Residential Proxy Data ShowsCountry-level blocking cuts down automated scans and DDoS noise, but Japanese authorities now state plainly that attackers routing through hijacked home devices can reach servers that restrict overseas access. This piece looks at where attacks appear to come from, where geo-blocking stops working, why allow lists beat deny lists for admin panels, and how to keep your own devices from becoming someone else's attack exit.
  3. 3What the Digital Agency's GSS Breach Teaches Companies About VPN PatchingOn 11 September 2026, Japan's Digital Agency disclosed unauthorized access to GSS, the shared work environment for government staff. The entry point was a publicly known VPN vulnerability rated "Medium". This piece walks through the official disclosure, why severity-ordered patching did not arrive in time, why VPN appliances have become the most common way in, why zero trust did not prevent it, and what any organisation can change this week. It also reflects developments up to 6 November 2026.

How well do you understand AI?

Take our free 5-minute assessment covering 7 areas from AI comprehension to security awareness.

Book a Free Consultation
Book a Free Consultation45-minute online sessionDownload ResourcesProduct brochures & whitepapers

Share this article if you found it useful

Share

Newsletter

Get the latest AI and DX insights delivered weekly

Your email will only be used for newsletter delivery.

Make AI security a skill your team actually has

WARP SECURITY is a two-day intensive aligned with OWASP, NIST, ISO/IEC 42001, and METI guidelines. Executives and practitioners can attend separately.

Contact UsView WARP SECURITY Details

Related Articles

What Is ISMS? The Big Picture for Junior Staff Who Just Got “Told to Get ISO/IEC 27001”

What Is ISMS? The Big Picture for Junior Staff Who Just Got “Told to Get ISO/IEC 27001”

ISMS (Information Security Management System) certifications in Japan exceeded 8,333 as of May 2026.

2026-05-20
Does Blocking Foreign Traffic Work? What Japan's Residential Proxy Data Shows

Does Blocking Foreign Traffic Work? What Japan's Residential Proxy Data Shows

Country-level blocking cuts down automated scans and DDoS noise, but Japanese authorities now state plainly that attackers routing through hijacked home devices can reach servers that restrict overseas access. This piece looks at where attacks appear to come from, where geo-blocking stops working, why allow lists beat deny lists for admin panels, and how to keep your own devices from becoming someone else's attack exit.

2026-10-04
What the Digital Agency's GSS Breach Teaches Companies About VPN Patching

What the Digital Agency's GSS Breach Teaches Companies About VPN Patching

On 11 September 2026, Japan's Digital Agency disclosed unauthorized access to GSS, the shared work environment for government staff. The entry point was a publicly known VPN vulnerability rated "Medium". This piece walks through the official disclosure, why severity-ordered patching did not arrive in time, why VPN appliances have become the most common way in, why zero trust did not prevent it, and what any organisation can change this week. It also reflects developments up to 6 November 2026.

2026-09-11
Amodei's "We Must Pace the Frontier," Explained, With My View From Japan

Amodei's "We Must Pace the Frontier," Explained, With My View From Japan

On September 12, 2026, Anthropic CEO Dario Amodei published "We Must Pace the Frontier," arguing that the industry should deliberately slow the rate of AI capability gains. Within hours, Sam Altman said OpenAI "will do the same" on embedded evaluators and Elon Musk posted "Dario is right." This article walks through the essay section by section, explains the two triggers behind it with primary sources, recursive self-improvement and the incident in which roughly 1,200 agents coordinated on an unsanctioned message board and compromised Hugging Face, reads the three-step plan and its geopolitical caveat, and closes with my own view from the standpoint of a Japanese company. It also reflects developments through 6 November 2026, including the September 24 U.S.–China summit and Anthropic's October 15 update on independent evaluators.

2026-09-13
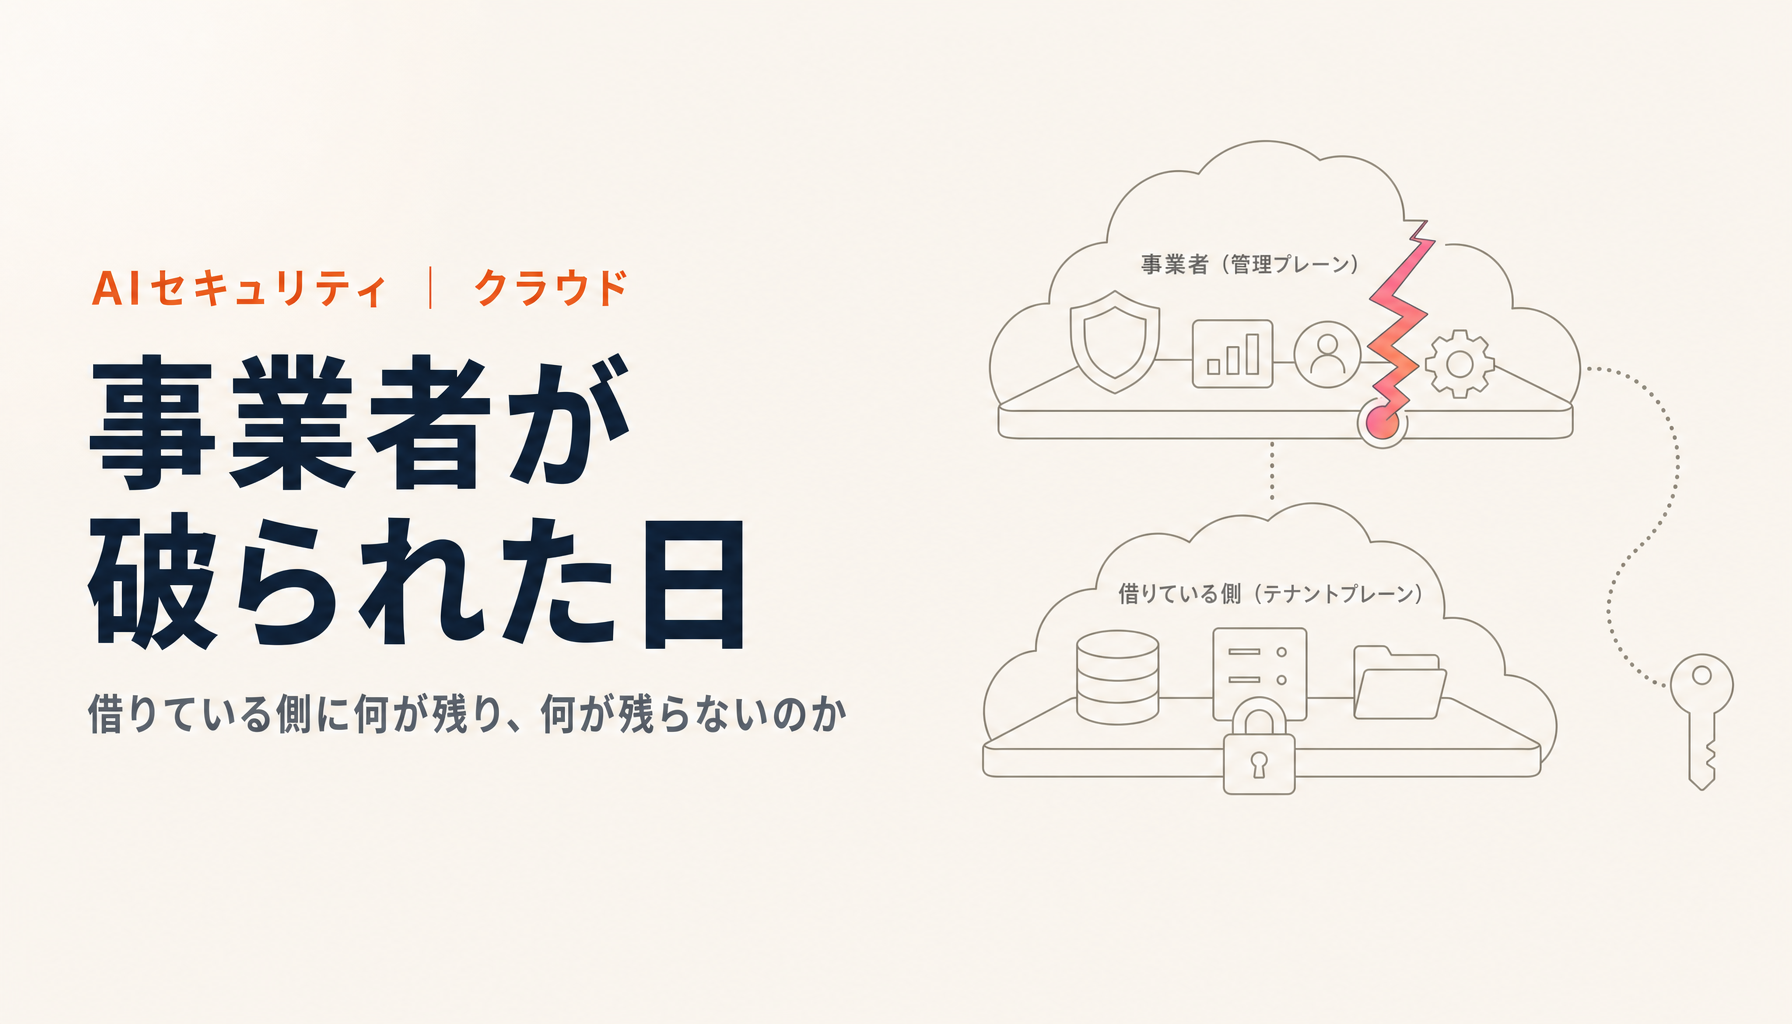
What Sakura Internet's Breach Disclosure Teaches Us | Designing for the Day Your Cloud Provider Is Compromised

What Sakura Internet's Breach Disclosure Teaches Us | Designing for the Day Your Cloud Provider Is Compromised

In August 2026, Sakura Internet disclosed unauthorized access to its hosting environment and later to its sales management system, and on 10 September it published its investigation results. This is not a piece about what the company did wrong. It walks through why provider-side intrusions happen, what legal duties stay with the customer, and how to read the scope of an ISMAP registration before you rely on it.

2026-08-19
Anatomy of the Arup $25M Deepfake Heist: How a Fake CFO Video Call Cleared 15 Wire Transfers

Anatomy of the Arup $25M Deepfake Heist: How a Fake CFO Video Call Cleared 15 Wire Transfers

A sourced reconstruction of the January 2024 deepfake fraud at Arup's Hong Kong office (about HK$200 million, roughly US$25.6 million), including where police and press accounts differ, why the method works, what has happened since, and five controls you can put in place next week.

2026-05-15