TIMEWELL
Solutions
Free ConsultationContact Us
TIMEWELL

Unleashing organizational potential with AI

ISO/IEC 27001 (ISMS) certification mark (SGS / ISMS-AC)

ISO/IEC 27001:2022 certified Certificate No. JP26/00000255 Scope: Planning, development and operation of SaaS products utilizing AI technology

Services

  • ZEROCK
  • TRAFEED
  • TIMEWELL BASE
  • WARP
  • WARP 1Day
  • WARP NEXT Corporate
  • WARP BASIC
  • WARP ENTRE
  • Alumni Salon
  • WARP for Schools
  • Alumni Ventures
  • FDE
  • AI Consulting
  • EMC GLOBAL

Company

  • About Us
  • Team
  • Why TIMEWELL
  • News
  • Contact
  • Free Consultation

Content

  • Insights
  • Knowledge Base
  • Case Studies
  • Whitepapers
  • Events
  • Solutions
  • AI Readiness Check
  • ROI Calculator

Legal

  • Privacy Policy
  • Manual Creator Extension
  • WARP Terms of Service
  • WARP NEXT School Rules
  • Legal Notice
  • Security
  • Anti-Social Policy
  • ZEROCK Terms of Service
  • TIMEWELL BASE Terms of Service

Newsletter

Get the latest AI and DX insights delivered weekly

Your email will only be used for newsletter delivery.

© 2026 株式会社TIMEWELL All rights reserved.

Contact Us
HomeColumnsTagsIncident Response
Tag

Incident Response

Articles about "Incident Response"

4 articles

4 articles

Lessons From the GMO Breach: What Government, Companies and Individuals Should Do Now
AI Security

Lessons From the GMO Breach: What Government, Companies and Individuals Should Do Now

This article lays out what happened in the October 2026 unauthorized access to GMO's Onamae.com Desktop Cloud, using GMO's official announcements and press reports, and then explains what we can learn from it in three roles: government, companies and individuals. It is written in plain language for beginners and ends with actions you can take today.

2026-11-06Ryuta Hamamoto
Hit by a Cyberattack in Japan? First Steps for Individuals and Companies
AI Security

Hit by a Cyberattack in Japan? First Steps for Individuals and Companies

In late September and early October 2026, several major South Korean banks disclosed cyberattacks. If the same happened in Japan, what should customers and companies do first? Working from primary sources, this article covers self-reporting to Japan's three credit bureaus, police and consumer hotlines, the deadlines for breach reports to the Personal Information Protection Commission, and reporting under Japan's new active cyber defense law.

2026-10-04Ryuta Hamamoto
What the Digital Agency's GSS Breach Teaches Companies About VPN Patching
AI Security

What the Digital Agency's GSS Breach Teaches Companies About VPN Patching

On 11 September 2026, Japan's Digital Agency disclosed unauthorized access to GSS, the shared work environment for government staff. The entry point was a publicly known VPN vulnerability rated "Medium". This piece walks through the official disclosure, why severity-ordered patching did not arrive in time, why VPN appliances have become the most common way in, why zero trust did not prevent it, and what any organisation can change this week. It also reflects developments up to 6 November 2026.

2026-09-11Ryuta Hamamoto
What Sakura Internet's Breach Disclosure Teaches Us | Designing for the Day Your Cloud Provider Is Compromised
AI Security

What Sakura Internet's Breach Disclosure Teaches Us | Designing for the Day Your Cloud Provider Is Compromised

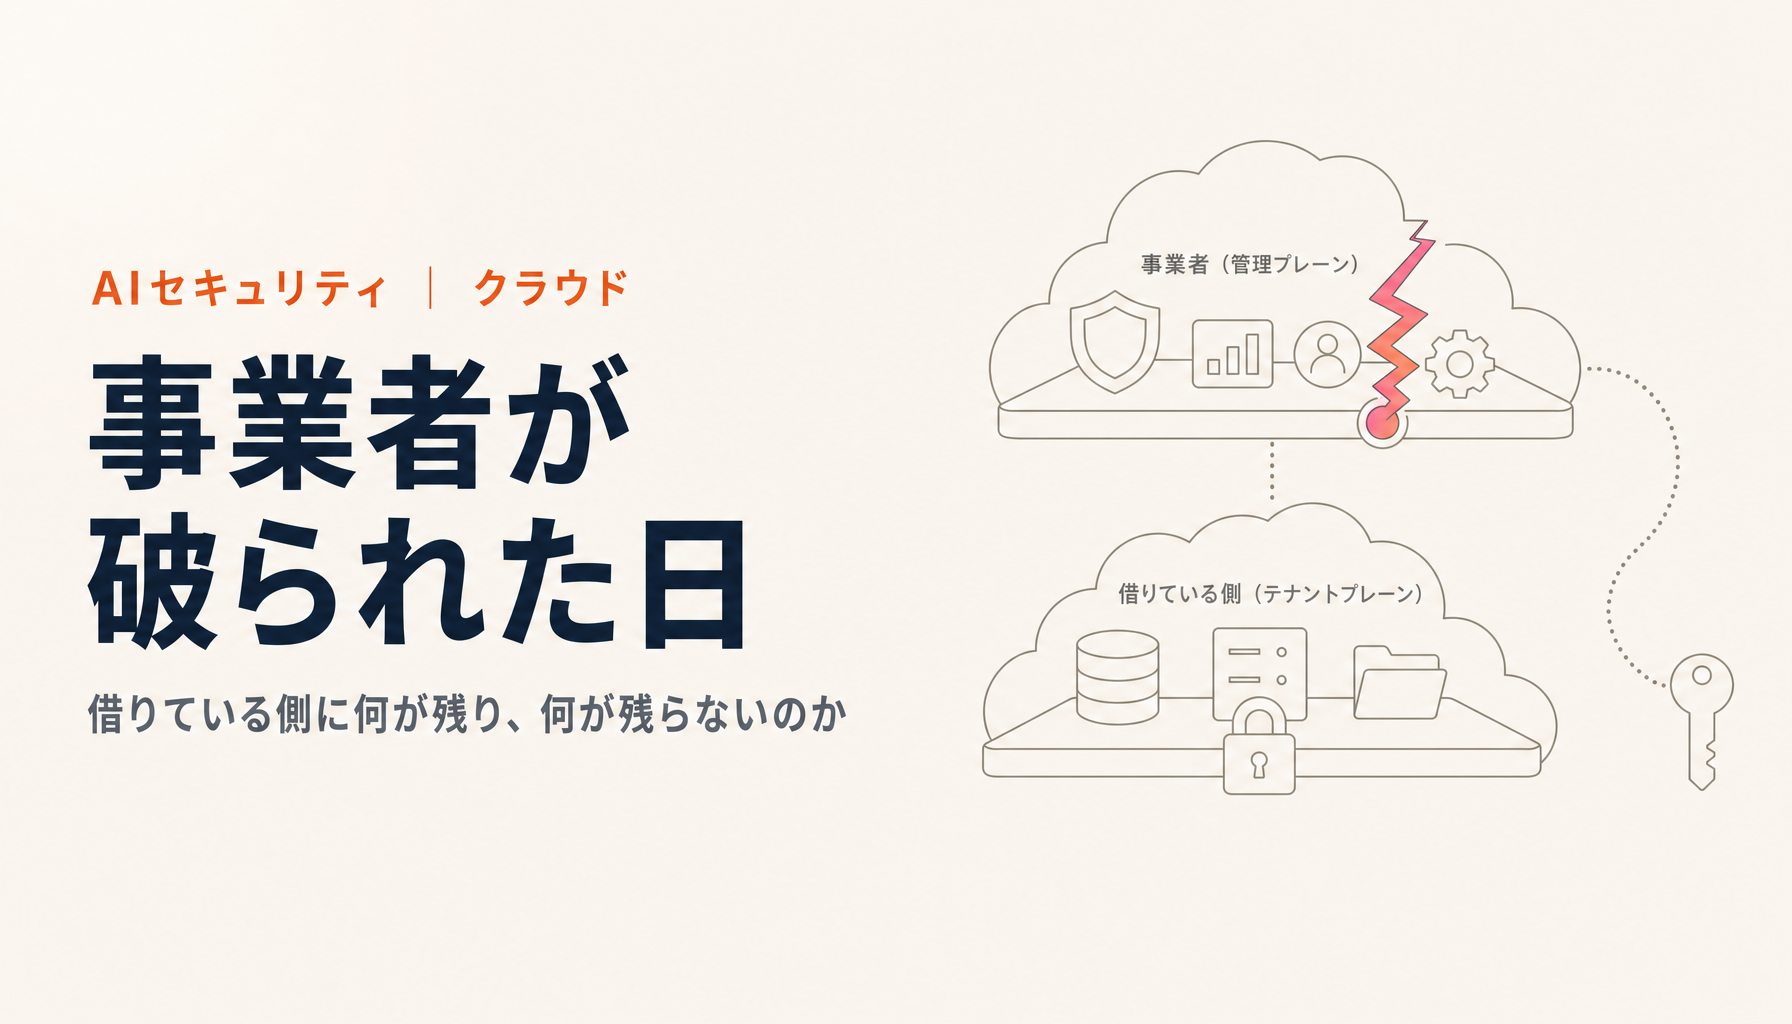
In August 2026, Sakura Internet disclosed unauthorized access to its hosting environment and later to its sales management system, and on 10 September it published its investigation results. This is not a piece about what the company did wrong. It walks through why provider-side intrusions happen, what legal duties stay with the customer, and how to read the scope of an ISMAP registration before you rely on it.

2026-08-19Ryuta Hamamoto

Related Tags

AI Security(4)WARP SECURITY(4)Unauthorized Access(3)Ransomware(2)GMO(1)For Executives(1)Cyberattacks(1)Data Breach(1)Identity Documents(1)Breach Reporting(1)VPN(1)Vulnerability Management(1)Zero Trust(1)Cloud Security(1)ISMAP(1)
View all tags