[2026 Edition] Customer Due Diligence (End-User Screening) in Practice — How to Cross-Reference the Foreign User List and Entity List
This is Hamamoto from TIMEWELL.
"Can we really trust this counterparty?"
When conducting international business, the reliability of your counterparties is critically important. In export control in particular, you have an obligation to verify that counterparties are not organizations involved in the development of weapons of mass destruction or military institutions.
Failing to carry out this verification creates risk of violating Japan's Foreign Exchange Act — and "I didn't know" will not be accepted as a defense.
This article explains the specific methods for customer due diligence (end-user screening / customer screening) in practical terms, including how to use Japan's Foreign User List and the U.S. Entity List.
The short version: the starting point for a Japanese exporter is the catch-all control's check on end-use and end-user, together with METI's Foreign User List. Since 9 October 2025, concern about conventional weapons development is part of that check, and the Foreign User List has grown to 835 entities across 15 countries and regions. Not appearing on a list, however, is not proof that a counterparty is safe. After list cross-referencing come web research, direct confirmation where needed, and record-keeping. This article covers the screening and verification routine; it does not decide whether a particular item needs a license. That judgment stays with your own export control officer.
Put your list-checking routine into a written, fill-in procedure: The lists discussed here — Japan's Foreign End User List, the US Entity List, the SDN and the rest — organized as five systems (US OFAC, US BIS, the EU, the UK, the UN) plus Japan's list, with fields for which official source to check, how often, and against what. The 50% / ownership-control tests and Red Flags are included, so you can fix a routine that currently varies by person into an internal standard. → Download the Five Sanctions-List Systems Screening Procedure (2026) (Free. Registration with your company name and work email address is required.)
If you are reviewing export-control operations or classification workflows, download the TRAFEED product catalog (PDF) or contact us.
Summary (What You'll Learn from This Article)
- Obligation to conduct customer due diligence: Exporters are required to verify intended end-use and end-user
- Foreign User List: METI's list of organizations of concern (835 entities, applied from 9 October 2025)
- Entity List: The U.S. BIS-managed list of export-restricted parties
- How to conduct investigations: Combining list cross-referencing, web research, and direct verification
- The scale of the task: Cross-referencing multiple lists, multilingual handling — a massive workload
How to Check the Entity List Right Now (the Short Answer First)
If you came to this article looking for where to find the latest version of the Entity List, here is the answer up front. As of 6 November 2026, the current Entity List can be checked free of charge on official U.S. government sites.
| Where to check | Location | When to use it |
|---|---|---|
| Consolidated Screening List (CSL) | trade.gov/consolidated-screening-list | Cross-searches the Entity List and other major U.S. restricted-party lists at once. In practice, start here |
| BIS official site | bis.gov | The agency that administers the Entity List. Amendment notices and guidance can be traced from here |
| Legal source text | eCFR, Supplement No. 4 to Part 744 of the EAR | The authoritative version. Consult it whenever a CSL search result leaves any doubt |
That said, searching counterparties one by one on official sites has real limits. The Entity List is updated on a rolling basis, and you also need to track name variations — abbreviations, local-language names — plus subsidiaries and affiliates. How to automate this manual work is covered in the second half of this article.
Replace siloed classification work with AI.
METI's FY2024 data shows 52% of foreign exchange law violations stem from classification errors. Download the TRAFEED product catalog covering features and rollout.
Table of Contents
- What Is Customer Due Diligence (End-User Screening)?
- Why Is Customer Due Diligence Necessary?
- How to Use the Foreign User List
- The U.S. Entity List and Consolidated Screening List
- Step-by-Step Customer Due Diligence Process
- How to Identify Suspicious Transactions (Red Flags)
- How to Streamline Customer Due Diligence with AI
What Is Customer Due Diligence (End-User Screening)?
Definition
Customer due diligence (end-user screening) is the process of verifying the intended end-use and end-user of exported goods or provided technology, and reviewing whether any national security concerns exist.
In English this is also called "Customer Due Diligence," "End-User Screening," or "Customer Screening."
Three Elements to Verify
Customer due diligence involves verifying three elements:
| Element | What to verify |
|---|---|
| End-Use | What the exported item will be used for |
| End-User | The organization or individual who will actually use it |
| Intermediary | Trading companies or agents in the transaction chain |
Where Customer Due Diligence Fits in Export Control
Customer due diligence occupies the following position in the export control process:
[Step 1] Export Classification (List Control Check)
    ↓
[Step 2] Customer Due Diligence (End-Use and End-User Verification) ← Here
    ↓
[Step 3] Determining Whether a License Application Is Required
    ↓
[Step 4] Export and Shipment Control
Why Is Customer Due Diligence Necessary?
Legal Obligation
Japan's Foreign Exchange and Foreign Trade Act (FEFTA) asks for a license not only for listed items but also for unlisted goods when the intended use or the end-user raises concern (the catch-all control). In practice, verifying use and end-user is close to an obligation for the exporter.
Under the catch-all control for weapons of mass destruction, a license application is required in two cases:
| Requirement | Content |
|---|---|
| Objective requirement (Inform) | When notified by the Minister of Economy, Trade and Industry |
| Subjective requirement (Catch) | When the exporter itself becomes aware of a concern |
In other words, "I didn't know" is not a defense. Failing to investigate what you should have investigated is itself a problem.
A rule change on 9 October 2025 reshaped the conventional-weapons side as well. Even for unlisted general-purpose goods such as machine tools, integrated circuits and parts for unmanned aircraft, an exporter who itself judges that the goods are highly likely to be used in developing conventional weapons must now apply to the Minister of Economy, Trade and Industry. The end-use and end-user conditions that trigger an application were clarified, and even for exports to Group A countries, METI can inform the exporter where there is a risk of diversion through procurement by countries of concern1. Because the system asks the exporter to make the judgment, the record of how you checked a counterparty, and on what basis you decided, now carries more weight than it used to.
Risks if Violated
Exporting to a party of concern without conducting proper due diligence creates the following risks:
| Risk | Content |
|---|---|
| Criminal penalties | Individuals: up to 7 years' imprisonment or a fine of up to 20 million yen (up to 10 years and 30 million yen for certain categories tied to nuclear weapons and similar). Corporations: a fine of up to 700 million yen (1 billion yen for those categories). Where five times the value of the goods exceeds the cap, the fine can reach five times that value |
| Administrative sanctions | Export ban of up to 3 years, public disclosure of company name |
| Reputational damage | Collapse of social credibility |
| Transaction termination | Major business partners terminating transactions |
Liability Even for Negligence
FEFTA violations are subject to administrative sanctions even when they result from negligence. "I trusted the counterparty" or "I had no means to check" are not valid defenses.
How to Use the Foreign User List
What Is the Foreign User List?
The Foreign User List is a list published by Japan's Ministry of Economy, Trade and Industry (METI) identifying overseas entities where concerns about the development of weapons of mass destruction, or of conventional weapons, have not been dispelled. Entities whose dealings need to be checked for conventional weapons development were added from the version applied on 9 October 20251. It is not an embargo list; it is reference information for exporters.
| Item | Details |
|---|---|
| Jurisdiction | Ministry of Economy, Trade and Industry (METI) |
| Number of entries | 835 entities (announced 29 September 2025, applied 9 October 2025; up 87 from the previous version) |
| Covered countries | 15 countries and regions |
| Update frequency | As needed (the latest revision was October 2025; I found no later revision as of 6 November 2026) |
Countries and Regions on the List
The list covers entities in 15 countries and regions, including China, North Korea and Iran. The breakdown by country and the entity names change with each revision, so check METI's current list rather than relying on a summary.
How to Use the List
Step 1: Download from METI's website
The Foreign User List can be downloaded free of charge from METI's website.
Step 2: Cross-reference counterparty names
Cross-reference the names of your counterparties against the organization names on the list.
Step 3: Watch for name variations
Be alert to name variations such as:
| Pattern | Example |
|---|---|
| Language differences | English name vs. local language name |
| Abbreviations | University → Univ. |
| Old/new names | Organizations that have changed their names |
| Affiliated organizations | Subsidiaries, affiliated institutions |
How to Respond if a Match Is Found
Exporting to an organization on the Foreign User List requires a license application, unless it is clear that the export will not be used for the development of weapons of mass destruction or conventional weapons. The reverse does not hold: not being listed does not end the check, and METI's Q&A on the conventional-weapons catch-all makes the same point, that looking only at listed entities is not enough. Use and end-user still have to be confirmed separately. For the whole October 2025 revision, in order of end-use, end-user and inform requirements, see our summary of the catch-all revision.
The U.S. Entity List and Consolidated Screening List
Why You Also Need to Check U.S. Lists
What Japanese law asks of exporters is the catch-all check on end-use and end-user. The Foreign User List is reference information METI provides for that judgment, and Japanese law does not oblige you to screen against U.S. lists.
Even so, checking U.S. lists is recommended for the following reasons:
| Reason | Content |
|---|---|
| Secondary sanctions risk | Sanctions from the U.S. for transacting with U.S.-sanctioned parties |
| Re-export of U.S.-origin items | Products containing U.S. components are subject to U.S. law |
| Counterparty reliability | Appearance on a U.S. list is a warning signal |
| Global standard | Many companies check U.S. lists as a matter of course |
What Is the Entity List?
The Entity List is a list of export-controlled parties maintained by the U.S. Department of Commerce's Bureau of Industry and Security (BIS).
| Item | Details |
|---|---|
| Jurisdiction | U.S. Department of Commerce (BIS) |
| Number of entries | A large number of organizations (added and removed on a rolling basis) |
| Effect | Export prohibition for U.S.-origin goods and technology |
| Update frequency | As needed |
The Consolidated Screening List
The Consolidated Screening List is a "unified screening list" provided by the U.S. government.
It allows cross-search across multiple regulatory lists, enabling efficient verification:
| Lists Included | Administering Agency |
|---|---|
| Entity List | Department of Commerce (BIS) |
| SDN List | Department of the Treasury (OFAC) |
| Denied Persons List | Department of Commerce (BIS) |
| Unverified List | Department of Commerce (BIS) |
| Military End User List | Department of Commerce (BIS) |
| Others | Department of State, etc. |
How to Check
The U.S. government provides an online searchable tool:
- Access the Consolidated Screening List website
- Enter the counterparty name
- If a hit is returned, verify the details
For the full picture across U.S., UN, and Japanese lists, see our guide to the five sanctions list families.
A counterparty that is not on the Entity List can still be caught if a listed organization owns 50 percent or more of it, directly or indirectly. That is the design of BIS's Affiliates Rule (the 50 percent rule), whose application has been suspended for one year from 10 November 2025. The suspension runs to 9 November 2026, and the US and China have announced an extension to 10 January 2027. As of 6 November 2026, however, I could not find a BIS extension rule in a Federal Register search. If none is published, the rule returns on 10 November, so keep an eye on the date. How to count ownership (exactly 50 percent, aggregation, grandchild companies) is in our guide to counting under the BIS and OFAC 50 percent rules, and finding hidden Chinese subsidiaries is covered in why the BIS 50 percent rule is hard to apply.
Step-by-Step Customer Due Diligence Process
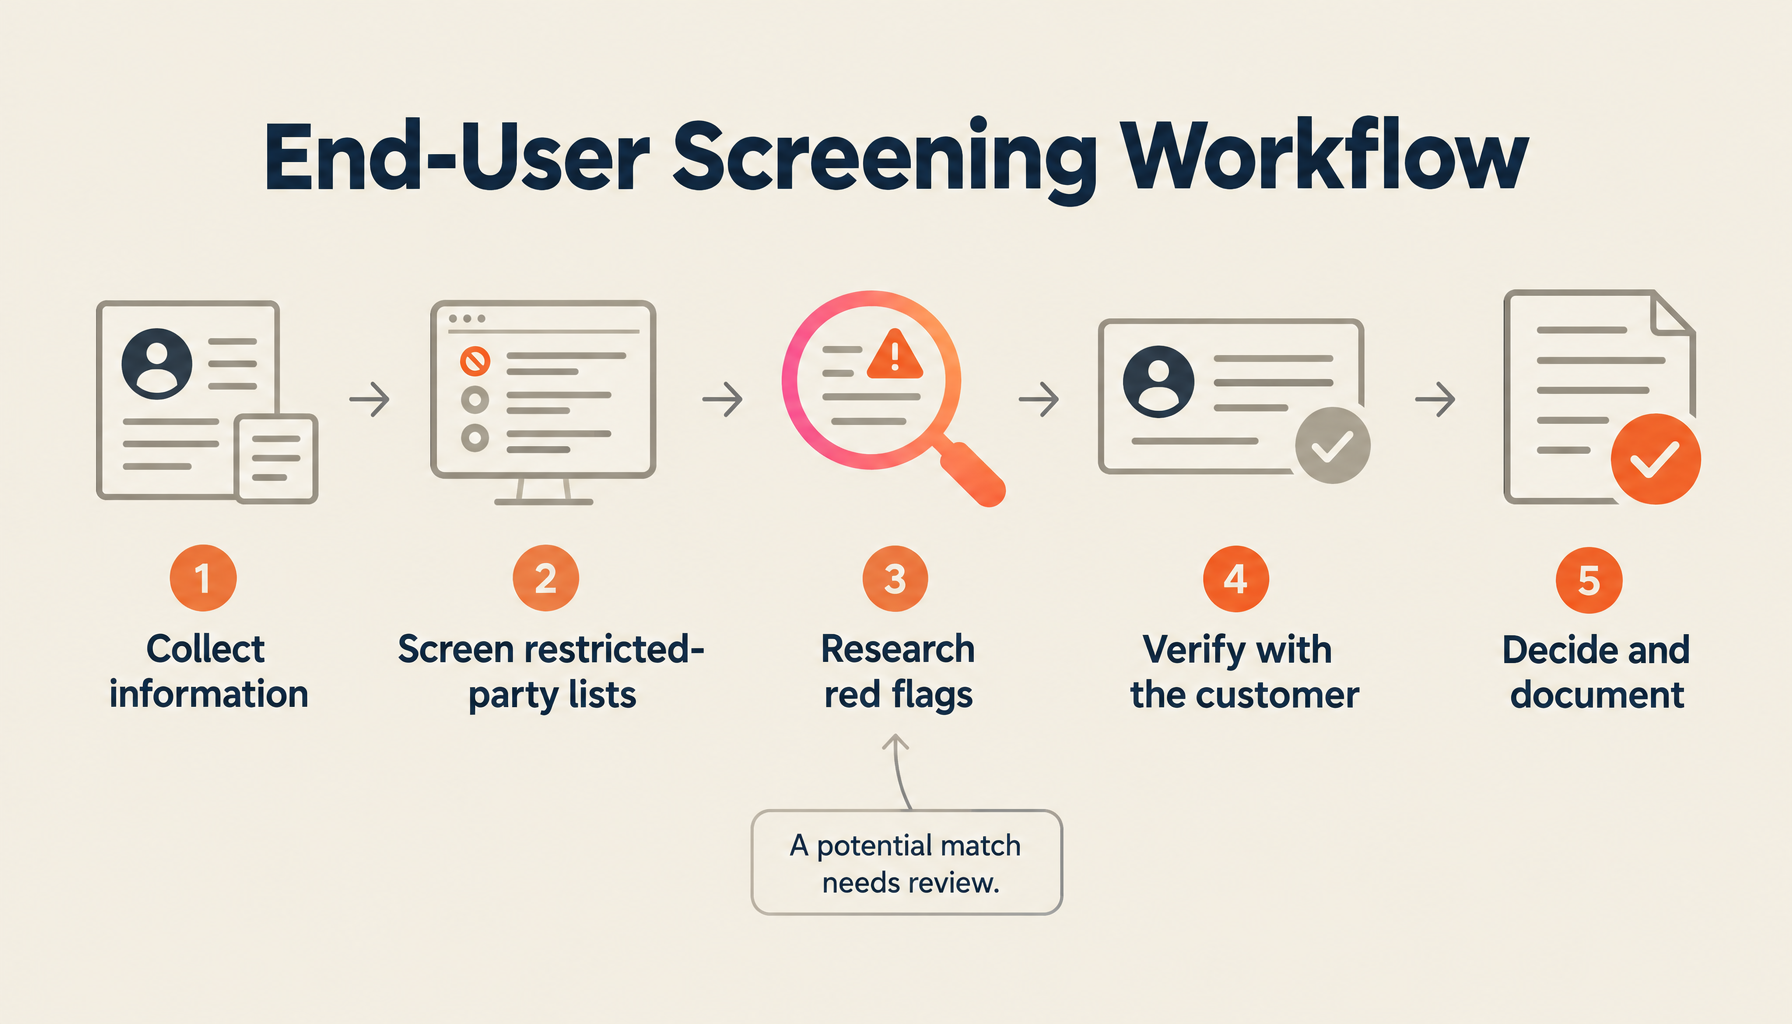
Overview of the Investigation Flow
[Step 1] Collect Basic Information
    ↓
[Step 2] Cross-Reference with Regulatory Lists
    ↓
[Step 3] Additional Research (Web research, etc.)
    ↓
[Step 4] Direct Verification (if needed)
    ↓
[Step 5] Determination and Documentation
Step 1: Collect Basic Information
First, collect the following information about the counterparty:
| Item | Content |
|---|---|
| Legal name | Corporate name (local language and English) |
| Location | Country, city, address |
| Industry | Business activities |
| Representatives | Executives, key persons |
| End-use | Intended purpose of the exported item |
Counterparty shareholders and beneficial owners are best checked at this stage, which makes the later steps easier. Why registration and disclosure regimes differ so much from country to country is explained in what a beneficial owner is.
Step 2: Cross-Reference with Regulatory Lists
Cross-reference against the following lists:
| List | Purpose |
|---|---|
| Foreign User List | Japanese legal obligation |
| Entity List | U.S. regulatory risk |
| SDN List | Sanctions target verification |
| UN Sanctions List | International sanctions verification |
Step 3: Additional Research (Web Research, etc.)
Even if not on any list, conduct the following additional research:
| Research method | What to check |
|---|---|
| Official website | Business activities, customers, business partners |
| News search | Presence of negative news |
| Registration information | Verify existence as a legal entity |
| Industry information | Reputation in the industry |
If you want to extend the check beyond the counterparty to its suppliers, UFLPA coverage and what it means for Japanese companies looks at it from the forced-labor angle.
Step 4: Direct Verification (if needed)
If concerns remain, verify directly with the counterparty:
| Item to verify | Specific questions |
|---|---|
| End-use | "What purpose will the product be used for?" |
| Re-export | "Do you plan to re-export to any third countries?" |
| Military connections | "Do you transact with military or military-affiliated institutions?" |
| Declaration | Obtain a declaration regarding end-use and re-export |
When to ask for a pledge or end-user certificate, and how to word it, is covered in our guide to end-user certificates and pledges.
Step 5: Determination and Documentation
Based on the investigation results, determine whether the transaction can proceed and create a record:
| Determination | Action |
|---|---|
| No concerns | Proceed with transaction; retain records |
| Concerns present | Request additional clarification; consider license application |
| Cannot proceed | Halt the transaction |
How to Identify Suspicious Transactions (Red Flags)
What Are Red Flags?
Red flags are warning signs indicating that a transaction may have national security concerns.
If any of the following signs are present, additional investigation is required.
Red Flags Related to the End-User
| Sign | Details |
|---|---|
| Company information unclear | No website; business activities unknown |
| Potential military connection | Relationship with Ministry of Defense, military, or military research institutions |
| Connection to listed organizations | Subsidiary or affiliate of an entity of concern |
| Suspicious location | Possible shell company |
Red Flags Related to End-Use
| Sign | Details |
|---|---|
| Cannot explain intended use | "I can't say what it's for" |
| Use and product do not match | Agricultural company purchasing high-performance measuring instruments |
| Excessive quantities | Orders disproportionately large relative to the scale of operations |
| Declining technical support | "We don't need any support" |
Red Flags Related to Transaction Conditions
| Sign | Details |
|---|---|
| Cash payment | Paying cash for high-value products |
| Unusual pricing | Willing to pay far above market price |
| Urgent ordering | "Please ship immediately" |
| Avoiding documentation | "No contract needed" |
Red Flags Related to Shipping
| Sign | Details |
|---|---|
| Shipping destination mismatch | Ordering entity and shipping destination are in different countries |
| Routing through free zones | Transit through regions with lax regulations |
| Multiple transit points | Unnecessarily complex routing |
| Special packaging requests | "Please package it so it won't stand out" |
How to Streamline Customer Due Diligence with AI
Challenges in Customer Due Diligence
Customer due diligence involves the following challenges:
| Challenge | Details |
|---|---|
| Multiple list cross-referencing | Foreign User List, Entity List, SDN List, etc. |
| Name variation handling | Multiple languages, abbreviations, old and new names |
| Identifying affiliated organizations | Tracking subsidiaries and affiliated institutions |
| Keeping up with list updates | Following frequent revisions |
| Enormous volume | All new and ongoing transactions must be covered |
There are real limits to what can be done manually.
The Reality of Investigation Workload
Estimated time per customer due diligence investigation:
| Task | Time required |
|---|---|
| Basic information collection | 15–30 minutes |
| List cross-referencing (multiple) | 30 minutes – 1 hour |
| Web research | 30 minutes – 1 hour |
| Documentation | 15–30 minutes |
| Total | 1.5–3 hours per case |
With 100 new counterparties per month, that's 150–300 hours per month.
How TRAFEED Solves This
TRAFEED is an export control-specialized AI agent that automates customer due diligence. It is, per our own research as of March 2026, the world's first AI agent in Japan's security export control domain, and holds a patent (Japanese Patent No. 7862062). It has been through a joint proof of concept with Okayama University, a national university, and as of July 2026 it has been adopted by more than 20 organizations across universities and companies.
| Function | Content |
|---|---|
| Multi-list screening | Batch screening across multiple lists |
| Name variation handling | Automatically detects similar names |
| Affiliated organization detection | Automatically identifies subsidiaries and affiliated institutions |
| Real-time updates | Automatically reflects list revisions |
| Automated report generation | Automatically creates investigation records |
In concrete terms, it supports same-day reflection of regulatory changes across jurisdictions, in-house approval workflows, advance due diligence on international students and new counterparties, and integration with major global paper, patent, and corporate databases.
One caveat worth stating plainly: TRAFEED's role ends at assembling the evidence without gaps. It is designed on the premise that the final export classification decision is made by your company's export control officer.
Lists Covered by Screening
TRAFEED integrates screening across the following lists:
| List | Country/Agency |
|---|---|
| Foreign User List | Japan (METI) |
| Entity List | United States (BIS) |
| SDN List | United States (OFAC) |
| Denied Persons List | United States (BIS) |
| Military End User List | United States (BIS) |
| UN Sanctions List | United Nations |
Conclusion
Key Points for Customer Due Diligence
- Legal obligation: Exporters are required to verify intended use and end-user
- Check multiple lists: Foreign User List + U.S. lists
- Additional research: Even if not on lists, verify that no concerns exist
- Red flags: Suspicious transactions require additional investigation
- Retain records: Document and retain all investigation results
What Companies Must Do
- Establish a customer due diligence process
- Conduct list cross-referencing without gaps
- Train employees to recognize red flags
- Retain investigation records appropriately
- Be prepared — "I didn't know" is not a defense
The Reality of Due Diligence Work
- 1.5–3 hours of work per case
- Multiple lists, multiple languages, name variation handling
- Keeping up with frequent list updates
- Manual processes alone have real limits
TIMEWELL Customer Due Diligence Support
TIMEWELL offers solutions to streamline customer due diligence (customer screening).
Consult About TRAFEED
- Implementation consultation: Diagnose your company's current due diligence process
- Demo: Experience AI-powered screening
- Customization: Optimization tailored to your industry and transaction patterns
"Is this company safe? AI delivers the answer."
For questions about streamlining customer due diligence, please feel free to reach out.
Reference Information
- METI Foreign User List
- Foreign User List revision, 29 September 2025 (METI announcement as carried by CISTEC, in Japanese)
- U.S. BIS Entity List
- Consolidated Screening List
- CISTEC Transaction Screening
Footnotes
-
METI announcement of the Foreign User List revision (29 September 2025, applied 9 October 2025), as carried by CISTEC (Japanese) https://www.cistec.or.jp/export/express/250929/1-20250929_1.pdf . The conventional-weapons catch-all revision was promulgated on 9 April 2025 and took effect on 9 October 2025, per METI's outline of the amended ordinances and a law-firm client alert ↩ ↩2