This is Hamamoto from TIMEWELL.
(21 November 2026) We corrected where the form of METI's "Exporter Overview and Self-Management Checklist (CL)" is set out. It is Form 3 of the circular on filing internal compliance programs, not the Guidelines for Handling Bulk Licenses.
(22 November 2026) In Step 3 we had described the transaction review role as "an employee in sales or legal" and the overall officer as "president or senior executive." Following METI's introductory guidance (p. 49), the minister's notice on internal compliance rules ((2)(iii)) and the compliance standards ordinance, the transaction review officer is now a director or similar who can decide independently of sales, with sales and legal gathering information, and the overall officer is chosen from among those who represent the company.
"Our overseas transactions have been growing, but our export control framework is completely undeveloped." "We were advised to build a framework during a METI outreach event, but we don't know where to start." "We've been told to create internal regulations, but there are no templates to work from." These are complaints I hear frequently from management departments at small and medium-sized enterprises.
METI provides free advisor dispatch and briefing sessions for SMEs. Yet the question of "what order should we tackle things in" — not having visibility into the overall picture — never goes away. Honestly, while government resources are comprehensive, their prioritization can be hard to discern.
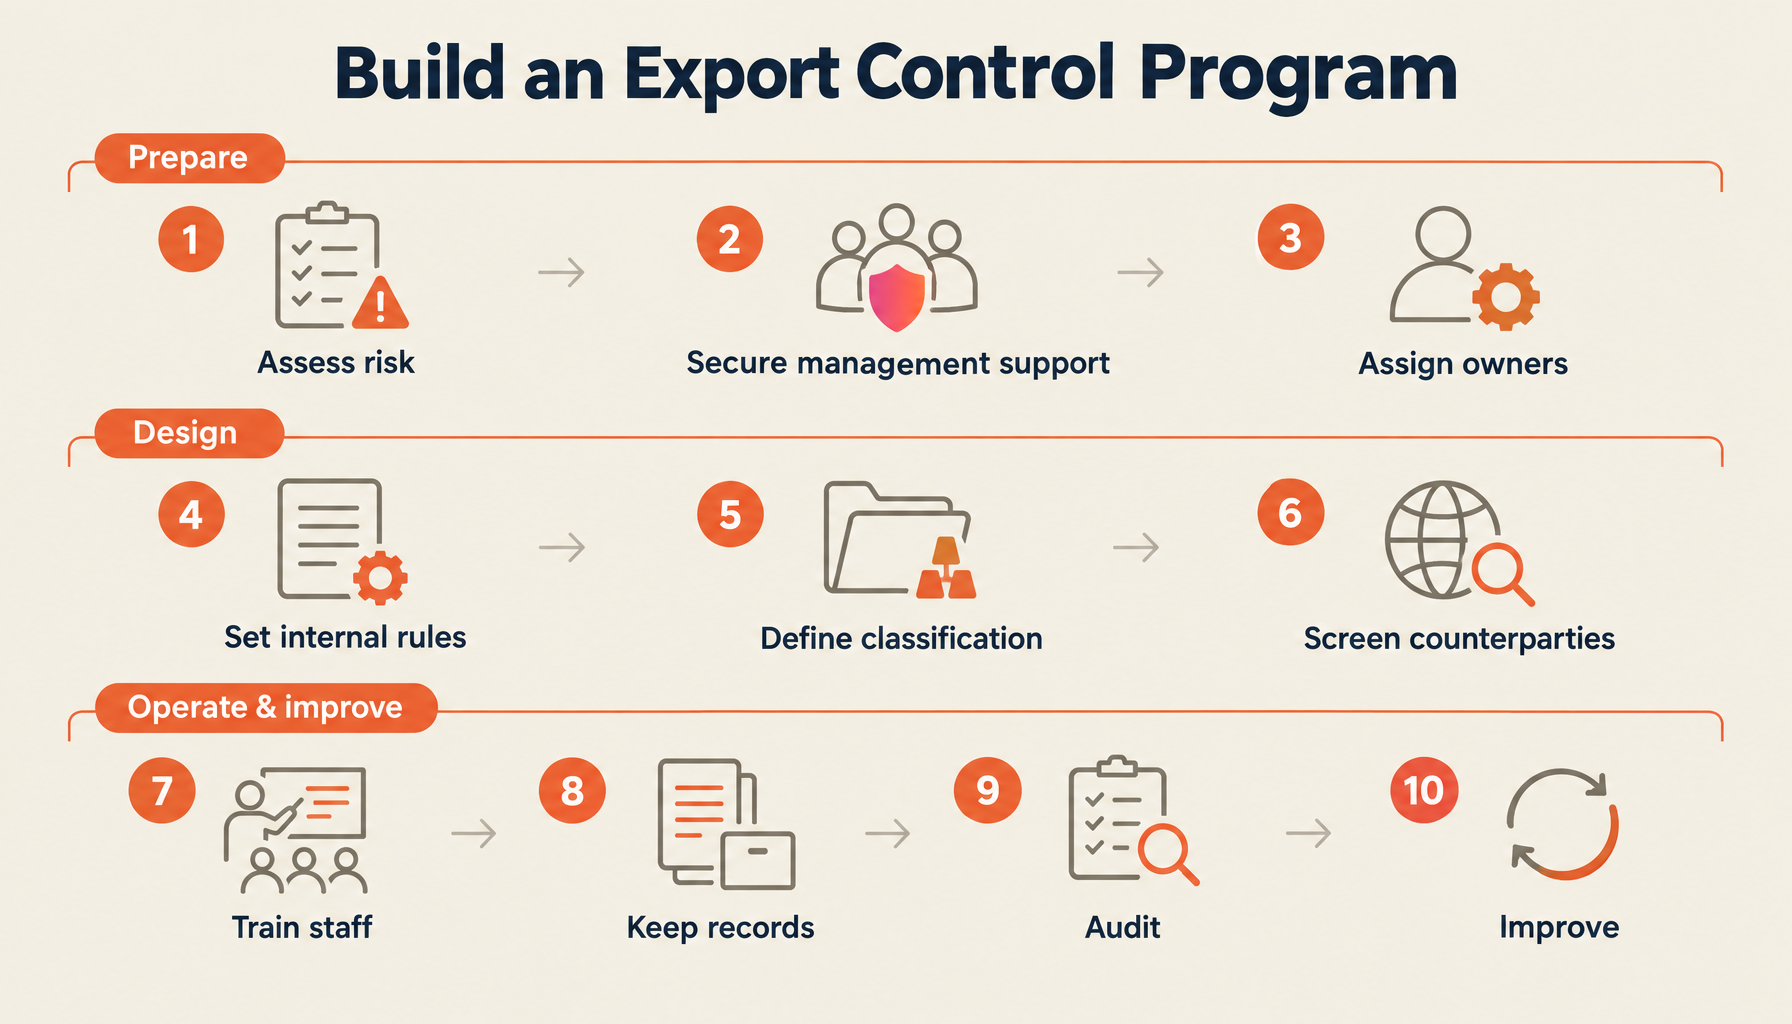
This article explains the 10 steps for building an export control framework from scratch, with a checklist of elements for internal compliance programs and references to METI guidelines.
A minimum version for part-time owners: the first 30 days
If you have been handed export control on top of another job, the first 30 days are covered in our guide to the first 30 days for a part-time export control owner: a week-by-week plan (asking for the responsible officer to be appointed at the very start of week 1), request templates, five checks for counterparties and an Excel plan. The 10 steps in this article are the full picture for building the framework properly after those 30 days.
What You Will Learn from This Article
- The overall picture of export control framework-building and how to progress through the 10 steps
- A checklist of elements to include in an internal compliance program (CP)
- How to use the official support resources provided by METI and CISTEC
- The "Exporter Compliance Standards" SMEs must grasp at a minimum (two items for all exporters, ten for businesses handling listed items)
- The operational cycle of running and improving the framework after it is built
Replace siloed classification work with AI.
METI's FY2024 data shows 52% of foreign exchange law violations stem from classification errors. Download the TRAFEED product catalog covering features and rollout.
Why SMEs Also Need an Export Control Framework
"We don't deal in weapons or military goods, so it doesn't apply to us." This assumption is dangerous.
FEFTA regulates not only weapons themselves, but also dual-use items that could be diverted to develop weapons of mass destruction or conventional weapons. High-precision machine tools, specific chemical substances, electronic components, software — products that appear to be purely civilian goods are not uncommonly subject to regulation.
Under the review of the supplementary (catch-all) controls that took effect on 9 October 2025, "specified items" designated by HS code in six categories, including machine tools and integrated circuits, became subject to the objective requirements (end-use and end-user) of the conventional-weapons catch-all even for general destinations. An inform requirement was also introduced for Group A destinations, limited to cases with a risk of diversion. See the three catch-all requirements.
A word on penalties as well. The criminal penalties under FEFTA depend on the provision. Unlicensed export or provision of technology for listed items and similar cases carries up to 7 years' imprisonment or a fine of up to 20 million yen (the two can be combined) for individuals, and a fine of up to 700 million yen for corporations. For goods and technology especially likely to be used in developing nuclear weapons and similar, the caps are 10 years or 30 million yen for individuals and 1 billion yen for corporations (FEFTA Articles 69-7 and 72). Fines can rise to five times the value of the goods. In addition, administrative sanctions including an export ban of up to 3 years may be imposed. This is at a level that affects business continuity itself.
Understanding the Exporter Compliance Standards
Before beginning to build your framework, familiarize yourself with the "Exporter Compliance Standards." These are the minimum standards that all exporters must comply with under FEFTA.
| Group | Item | Obligation or best effort |
|---|---|---|
| (i) All exporters | (a) Appoint a person responsible for checking whether items are controlled (classification officer) | Mandatory |
| Same | (b) Give staff engaged in exports guidance needed to comply with the law, including keeping them informed of the latest rules | Mandatory |
| (ii) Businesses that export or provide listed items as a business | (a) Appoint, from among the representatives, an officer who oversees export operations (general export control officer) | Mandatory |
| Same | (b) Define the authority and responsibility of the departments handling exports, and the relationship between them | Mandatory |
| Same | (c) Set classification procedures | Mandatory |
| Same | (d) Set procedures to check end use and end users, and check them under those procedures | Mandatory |
| Same | (e) At shipment, confirm the goods match the goods described in the documents | Mandatory |
| Same | (f) Set up an audit system and procedures and audit periodically | Best effort |
| Same | (g) Train the general officer and staff | Best effort |
| Same | (h) Where subsidiaries are involved, set up and periodically carry out guidance, training and checks for them | Best effort |
| Same | (i) Retain export-related documents for an appropriate period | Best effort |
| Same | (j) If a violation occurs or may have occurred, promptly report to the Minister of Economy, Trade and Industry and take recurrence-prevention measures | Mandatory |
The two items in group (i) apply to every exporter, including companies that handle no listed items. The ten items in group (ii) apply to businesses that export or provide listed items; items (f) to (i) are best-effort and the rest are mandatory (Article 1 of the Ministerial Ordinance on Exporter Compliance Standards, checked in the e-Gov text on 20 November 2026; the item letters here stand for the Japanese iroha order). The classification officer and the general officer may be the same person (Article 2). Even so, records of audits and training are what let you explain your framework if a violation occurs. It is unwise to think "it's just best-effort, so we don't have to do it."
The 10 Steps for Building an Export Control Framework
Step 1: Understand Your Current State and Inventory Your Company's Risk
The first thing to do is understand your company's actual export practices. What types of goods and technology are you exporting, and in what volumes? What countries and regions are the main export destinations? What are the industries and intended uses of your counterparties? Is there a current management workflow?
Perfection is not the goal at this stage. The objective is to make visible "what is being managed and what is not."
Step 2: Obtain Commitment from Management
An export control framework cannot function without the commitment of top management. The Compliance Standards ordinance requires anyone who exports list-controlled items as a business to appoint the overall officer "from among those who represent" the company (Article 1, item 2 (i)), and METI's introductory guidance explains that in an ordinary company the representative director must be designated as the chief officer (Edition 3.0, Chapter 4, I (3)). What Article 1, item 1 (i), which covers all exporters, requires is the appointment of a classification officer.
The most effective way to motivate management is to convey the specific risks of regulatory violations.
| Type of risk | Specific content | Basis / where to check |
|---|---|---|
| Criminal penalties | Individuals: imprisonment up to 7 years or a fine up to 20 million yen (10 years and 30 million yen for nuclear-weapons-related items). Corporations: up to 700 million yen (1 billion yen for nuclear-weapons-related items) | FEFTA Articles 69-7 and 72; see our guide to FEFTA penalties and cases |
| Administrative sanctions | A ban on exports and technology transfers for a period of up to 3 years (FEFTA Articles 53 and 25-2) | Published cases can be checked in METI's list of administrative sanctions |
| Reputational damage | Loss of trust from business partners and lenders when a case or sanction is reported | METI's annual analysis of FEFTA violation cases shows the causes and how cases came to light |
| Transaction termination | Exclusion from supply chain by major counterparties | Reviews of transactions with companies found to have inadequate management frameworks |
When briefing management, spelling out "up to a 1-billion-yen fine (nuclear-weapons-related; 700 million yen for ordinary listed items)" and "the export ban" makes the stakes concrete.
Step 3: Appoint an Export Control Officer and Staff
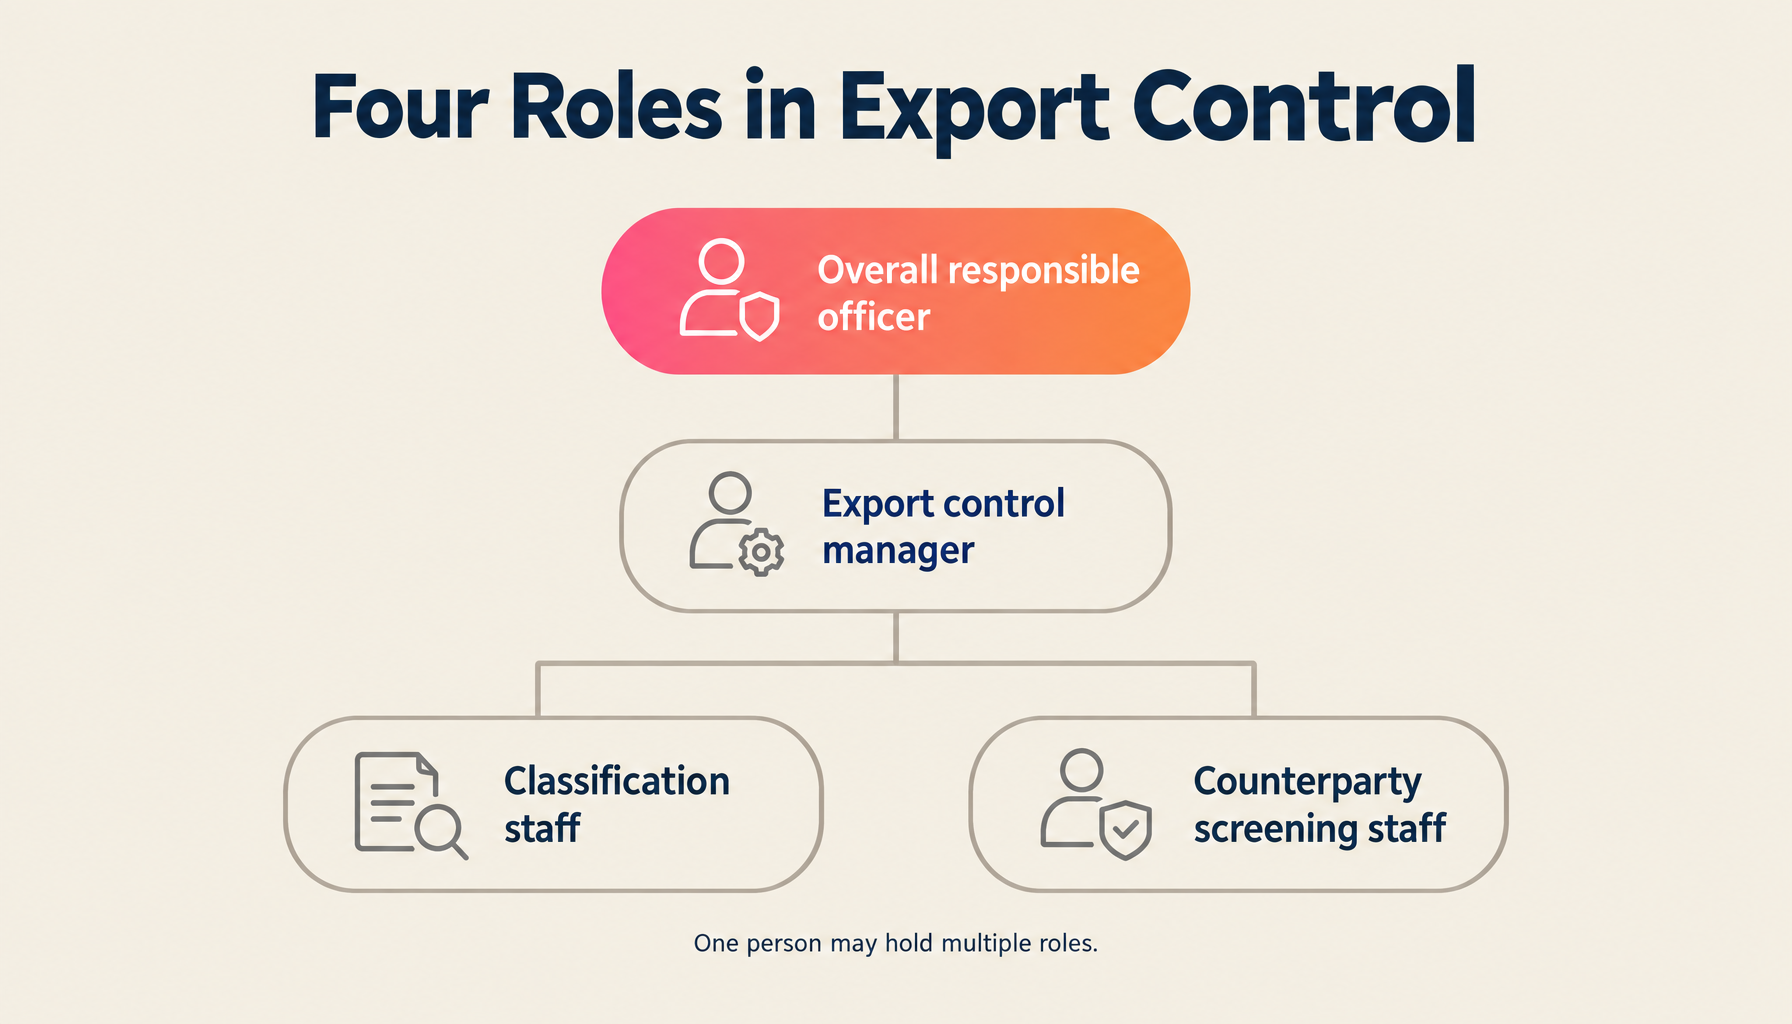
A dedicated person is ideal, but in SMEs, concurrent roles are the reality. Even so, clearly define the roles. The minimum required roles are four: an overall responsible officer (the representative director; the ordinance requires choosing this officer "from among those who represent" the company, so not just any senior executive), an export control manager (head of the management department), an export classification staff member (an employee with deep technical knowledge), and a transaction review officer (a director or similar who can decide independently of sales). METI's introductory guidance recommends that the transaction review officer be able to judge independently of the exporting department (sales and the like) and expects the officer to be chosen from among directors or similar, because the organization makes the final decision on the deal (p. 49). The minister's notice on drafting and reviewing internal compliance rules likewise calls for a director or above to be the final decision-maker in transaction reviews ((2)(iii)). Sales or legal staff gather counterparty information and pass it up. If a small company cannot fill each role separately, the guidance suggests the representative director may serve as both chief officer and transaction review officer (p. 49).
If it is difficult to have four separate people in an SME, concurrent roles are acceptable. However, operating without clarity on "who makes which decision" will result in issues during inspections and ambiguous accountability in an emergency.
Step 4: Formulate an Internal Compliance Program (CP)
It is efficient to use CISTEC's publicly available "Model CP" as a base, adapted to your company's actual circumstances. Six patterns are available, combining the management structure (a dedicated department, a designated officer, or direct management by the representative director) with the classification scope (whether the company has its own products). CISTEC notes that the patterns do not distinguish companies by sales, capital, or headcount.
The elements to include in the CP are as follows:
| Chapter | Program element | Content to specify |
|---|---|---|
| Chapter 1 | Purpose and scope | Purpose of the program, scope of covered operations |
| Chapter 2 | Management framework | Roles and authority of responsible officers and staff, organizational chart |
| Chapter 3 | Export classification procedure | Classification flow, format of classification certificates, approval process |
| Chapter 4 | Counterparty screening procedure | Intended use verification, end-user verification, screening criteria |
| Chapter 5 | License application procedure | Application flow to METI, supporting documents |
| Chapter 6 | Shipment management | Pre-shipment verification check, customs clearance procedures |
| Chapter 7 | Internal audit | Frequency, method, records |
| Chapter 8 | Education and training | Target personnel, frequency, content |
| Chapter 9 | Document management | Retention period, storage method, disposal rules |
| Chapter 10 | Violation response | Reporting route, reporting procedures to METI, recurrence prevention measures |
The Model CP provides only the skeleton. For practical operation, supplementary operating rules that specifically define "who does what and how" are also needed. Many companies skip this and assume "we have a CP, so we're covered" — but on-site inspections examine actual operations at the operating-rule level rather than the CP itself.
An outline for the first version of your CP: a Word document for companies without a full-time export control officer. Each of the ten articles has draft wording, a field to fill in and a worked example for a fictional Company A, with the matching item of the compliance standards ordinance and the page of METI's introductory guidance. It is our draft, not a METI form, so have your legal team review it. → Ten-article outline of an internal export compliance program (Word, in Japanese)
Step 5: Establish Operating Rules for Export Classification
Export classification is the core of the framework. Four rules must be documented: when to conduct the classification (when new products are developed, when an export transaction arises, when regulations change); what materials to use (specification sheets, measured data, regulatory matrix tables); the approval flow for classification results (from the classifier to the reviewer to the approver); and how and for how long to retain classification records.
Step 6: Build a Counterparty Screening Workflow
Establish the counterparty verification procedure. Lists to cross-reference against include: METI's Foreign User List, the U.S. BIS Entity List and SDN List, EU regulatory lists, and UN Security Council sanctions lists.
What to verify: the country where the counterparty is located and the destination country, the intended final use and end-user, whether there are any irregularities in the circumstances of the transaction, and the presence and role of intermediaries.
Step 7: Plan Education and Training Programs
Even if the framework is established, it will not function if the staff members who operate it in the field do not understand it.
| Target | Frequency | Content |
|---|---|---|
| Management | Once a year | Legal violation risks, latest regulatory trends |
| Export control department | At least twice a year | Practical export classification, practical counterparty screening |
| Sales department | Once a year | Items to verify at order intake, signs of risk |
| Technical department | Once a year | Technology transfer risks, deemed export |
| New employees | Upon joining | Overview of export control, internal rules |
METI's free briefing sessions (commissioned projects) and CISTEC's various training courses are useful means of incorporating external expertise at low cost.
Step 8: Build Document Management and Record-Keeping Systems
Retention of export-related documents is a best-effort item under the Exporter Compliance Standards (paragraph 2, item (ri) of Article 1 of the Ministerial Ordinance: "endeavor to retain ... for an appropriate period"). In the provisions I checked (FEFTA, the Foreign Exchange Order, the Export Trade Control Order, and the Export Trade Control Regulations), I could not find a rule imposing one fixed retention period, such as 5 years, on export documents generally. METI's introductory guidance (version 3.0) gives a guide of at least 7 years from the date of export or provision for items in rows 1 to 4, and at least 5 years for rows 5 to 16. Separately, anyone exporting goods as a business must keep customs-related books and documents (including invoices) for 5 years from the day after the export permit, under Article 94(2) of the Customs Act and Article 83(8) of its Enforcement Order. Set your own period so that it does not fall below either of these, and write it into your internal rules. Consider including the following in what you retain: export classification certificates, counterparty screening records, export licenses, contracts and invoices, end-use certificates, shipment records, internal audit reports, and records of education and training sessions.
Physical paper storage takes up space and has poor searchability, so consider digitization. For electronic data, measures to prevent tampering — such as timestamp management and access log management — are also necessary.
Step 9: Plan and Conduct Internal Audits
Conduct internal audits at least once a year. METI's "Exporter Overview and Self-Management Checklist (CL)", which is Form 3 of the circular on filing internal compliance programs and is submitted every July by companies that have filed a CP, is a useful reference for what to check.
Key points to examine in audits: Are operations being conducted in accordance with the CP? Are export classification records being properly maintained? Are there any cases where counterparty screening is being skipped? Are education and training being conducted as planned? Is document storage in appropriate condition?
The 2025 CL revision now requires documentation of the frequency and methods of audits. METI's Q&A says audits should in principle be conducted at least once a year, and, where a company's own audit department cannot do them, lists alternatives: a written self-audit (with review by the audit department or similar), an audit by someone in the same department who is not in charge of export control, a cross-audit between departments by their export control staff, or outsourcing to a group company or a third party knowledgeable about export control (Q&A on the CP filing circular, Q38 and Q39).
Step 10: Continuously Improve Through a PDCA Cycle
Building the framework is the start, not the finish. Laws are frequently amended, and your company's products and counterparties also change.
Here is an example annual schedule:
| Month | Activities |
|---|---|
| April | Formulate annual plan; review previous year |
| May | Education and training (1st session) |
| July | Submit self-management checklist (CL) |
| September | Verify legal amendments and review internal regulations |
| October | Conduct internal audit |
| November | Education and training (2nd session) |
| December | Formulate improvement plan based on audit results |
| January | Verify updates to Foreign User List |
| March | Compile improvement measures for the coming year |
Official Support Resources from METI and CISTEC
Here is a summary of the official resources available to SMEs — all either free or low-cost.
| Provider | Resource | Content | Cost |
|---|---|---|---|
| METI | Security Trade Control Guidance (Introductory Edition) | Guide covering framework-building through procedures | Free |
| METI | Outreach program | Advisor dispatch, individual consultation | Free |
| METI | Briefing materials (introductory to intermediate level) | Explanations of legal overview and amendment content | Free |
| CISTEC | Model CP | Template for internal regulations (six patterns, a brokering version, and a group-company version) | Free (Word files on the public page) |
| CISTEC | Guide to Export Classification | Explanation of classification procedures and case studies | Free for CISTEC members |
| Tokyo Chamber of Commerce and Industry | Export control framework-building support | Seminars, individual consultation | Free |
| JETRO | Security Trade Control Quick Reference Guide | Overview explanation for beginners | Free |
Summary
Building an export control framework does not require completing everything at once. A phased approach is realistic.
The first priorities: securing management commitment, appointing responsible officers and staff, and formulating basic workflows for export classification and counterparty screening. These are the areas directly tied to mandatory obligations.
The next phase: formally formulating internal regulations (CP), starting the education and training program, digitizing document management, and conducting the first internal audit.
After that: staying current with regulatory amendments, running a PDCA improvement cycle, and continuing to conduct audits regularly.
By leveraging METI's outreach program and CISTEC's Model CP, and using the power of available tools, a genuinely effective framework can be built even with limited resources. Rather than aiming for perfection and being paralyzed, taking the first step is the best strategy.
If you want to start by putting screening of your existing counterparties on a routine footing, you can contact us about TRAFEED. An overview of its features is in the TRAFEED product catalog (PDF).
References
- METI, "Security Trade Control Guidance (Introductory Edition), Edition 3.0" (March 2026)
- METI, "Promotion of Voluntary Management by Companies"
- METI, "Support for Small and Medium-Sized Enterprises (Outreach Program)"
- e-Gov, "Ministerial Ordinance Establishing the Exporter Compliance Standards" (METI Ordinance No. 60 of 2009; in Japanese)
- METI, circular on filing internal compliance programs (Yushutsu Chuijiko 17 No. 9; Form 3 is the CL; in Japanese)
- METI, Q&A on the CP filing circular (May 2, 2025; Q38 and Q39 cover audit frequency and methods; in Japanese)
- CISTEC, "Introduction to the Model CP"
- CISTEC, "Exporter Compliance Standards — Your First Step!"
- CISTEC, "For Small and Medium-Sized Enterprises"
- Tokyo Chamber of Commerce and Industry, "Export Control Framework-Building Support"
- JETRO, "Security Trade Control Quick Reference Guide"
Related Articles
- 5 Steps to Streamline Export Classification
- List controls vs catch-all controls: a comparison table and when a license is needed even for non-listed items
- Practical Compliance Checklist for U.S. EAR (Re-Export Controls)
- Export Control on Top of Your Day Job in Japan: The First 30 Days and Five Counterparty Checks